-
Network Security Equipment Application Platform
As there are so many different network security tasks and tools for each of them, this review lists exceptional tools that fall into each of the defense strategies that you will need to deploy. None of them cover ever.
-
Slovenia Network Security Equipment SFP
Small Form-factor Pluggable (SFP) is a compact, hot-pluggable network interface module format used for both telecommunication and data communications applications. An SFP interface on networking hardware is a modular slot for a media-specific transceiver, such as for a fiber-optic cable or a copper cable. The advantage of using SFPs compared to fixed interfaces (e.g. modular connector. SFP typesSFP transceivers are available with a variety of transmitter and receiver specifications, allowing users to select the appropriate transceiver for each link to provide the required optical or electrical reach over. Quad Small Form-factor Pluggable (QSFP) transceivers are available with a variety of transmitter and receiver types, allowing users to select the appropriate transceiver for each link to provide the required optical reach over. SFP sockets are found in, routers, firewalls and. They are used in Fibre Channel and storage equipment. Because of their low cost, low profile, and ability to provide a c.
[PDF Version]
-
What are the components of network security devices
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. They include firewalls, intrusion prevention systems, VPN gateways, and other tools that safeguard data across network connections. These devices act as barriers between your network and the outside world, analyzing and filtering traffic.
-
Substation network security equipment
Substation security refers to the measures and technologies used to protect critical electrical infrastructure from malicious acts. Unique combinations of access, video security, alarm and sensor systems help to ensure the reliability of the power grid by mitigating substation. Physical security requires a reliable, secure, high-performance communications network between security devices (sensors, cameras, key pads, lights, etc. ) and computers located in the utility's operations center. Adding network communications to existing substations to extend reach to the various. This document is a guideline to design a substation based on SIPROTEC and SICAM products in a secure manner.
-
What is a network security equipment provider
Network security providers play a essential position in safeguarding companies from cyber threats and making sure the integrity of their digital infrastructure. These providers provide a big selection of innovative products and solutions designed to locate, prevent, and mitigate. Network security services are designed to protect internal company infrastructures and connected devices from undesired access, mishandling, and attacks. Hyve Managed Hosting — Best with direct-to-engineer support 2. Trustwave — Best for PCI compliance 3. It combines hardware, software, and expert resources to ensure network integrity and prevent breaches.
-
Network security equipment integration testing
During network integration testing, engineers simulate real-world scenarios to evaluate the network's performance, reliability, and scalability. This article explores the multifaceted aspects of IT system testing. In today's fast-paced, technology-driven world, network admission control (NAC) and continuous integration (CI) are essential components for maintaining robust security protocols within enterprise networks. By incorporating Internet testing systems into your CI environment, businesses can mitigate. Regular testing, integration with DevOps/CloudOps, combining automation with human expertise, and partnering with experts like Zymr, ensure enterprises stay resilient against evolving AI-driven and cloud-focused threats. In today's connected world, every enterprise depends on networks- from. Want to ensure your endpoint security system works flawlessly? Here's how: Integrate Tools: Combine EDR, SIEM, and threat intelligence for seamless monitoring and response across all devices. Test Effectively: Validate functionality, security, and performance without disrupting operations.
[PDF Version]
-
Network security equipment and environment security
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. They include firewalls, intrusion prevention systems, VPN gateways, and other tools that safeguard data across network. Physical and environmental security controls are implemented to protect the facility housing system resources, the system resources themselves, and the facilities used to support their operation. The term physical and environmental security, as used in this chapter, refers to measures taken to. How to design, use, and maintain secure networks. Networks are fundamental to the operation, security and resilience of many organisations. Cybercriminals deploy ransomware, AI-powered attacks, and advanced persistence tactics targeting critical data and infrastructure.
[PDF Version]
-
How to hide applications on a network terminal box
This is achieved by granular access control of the installed applications through App Masking Rules. These rules can be used to completely hide the application in an user runtime, so that it no longer appears in the file system, registry or under programs and features. How to map specific folder from a user's PC into a RAS session. By enabling these settings you can ensure that users do not inadvertently access data stored on other drives, or delete or damage. Hello, I am setting up a server 2008, TS RemoteApp box. I am having a slight security issue maybe one of you have seen before. I need to box locked down to where they can't browse anything except maybe a mapped drive like T:downloads. (Mapped drive set via user profile in AD via “Home Folder:. If an answer to your question is correct, click on "Verify Answer" under the "More" button. The answer will now appear with a checkmark. Is there some special terminal command that will hide an open application (essentially the equivalent of typing ⌘ + H from inside the application)? Something like this is a pretty rough start.
[PDF Version]
-
Network server rack noise
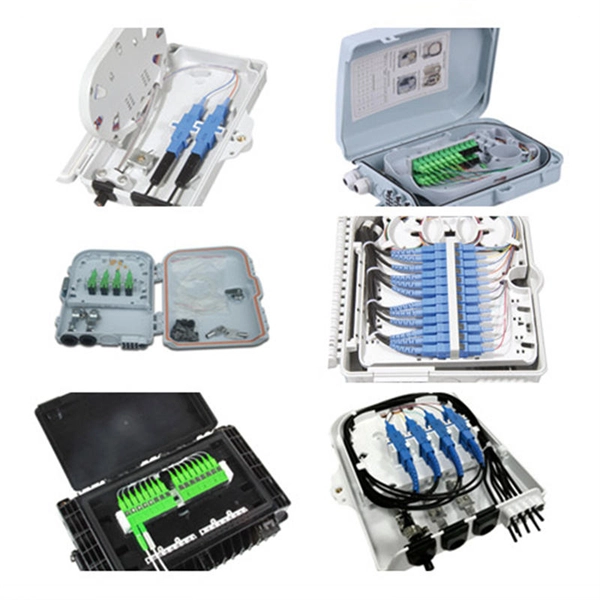
In this guide, we'll walk you through the do's and don'ts of soundproofing your server rack and demonstrate tools and techniques that actually work. We'll cover how new soundproof cabinets not only reduce noise but also help with heat management, airflow, and better securing your. High noise levels can create an uncomfortable working environment and signify inefficiencies that may affect your equipment or power usage. Server noise. Additionally, loud fan noise can disrupt your entire household. Furthermore, you'll learn simple tricks that work in real homes. “Proper. In the digital age, server rooms and data centers are the pulsating hearts of modern enterprises, housing critical IT infrastructure that powers operations.
-
How many devices should be placed in a 42u network rack
Theoretically, a 42U rack can accommodate: 10 servers in 4U format. However, in practice, some space is occupied by additional components such as PDUs, switches, cable management panels, and monitoring systems. As a result, the actual usable capacity is 10–15% lower. How to Choose a 42U Server Rack Cabinet for Your Data Center or Server Room Quick Specs – 42U Server Rack Cabinet Overview A fully loaded 42U server rack cabinet has the capacity for over 3000 lbs of networking equipment, averages 5. 7 kW per rail of power while fitting into a modest 78 inch tall. How many servers can you have on a 42U rack? The total amount of U-height available in a 42U high server rack is 42 × 1U. This is for a fully populated server cabinet and in. The standard size of the server rack is the 42U rack or 42 rack units, as it is commonly referred to. Individual rack units are typically about 1. For example, although a 42U. If you're installing switches, UPS units, patch panels, or edge servers in an office, colo space, or small data hall—start with this: choose a 42U floor-standing rack with front/rear doors, ≥60 cm depth, and tool-less vertical mounting rails.
[PDF Version]
-
Invisible fiber optic cable network cable connection method
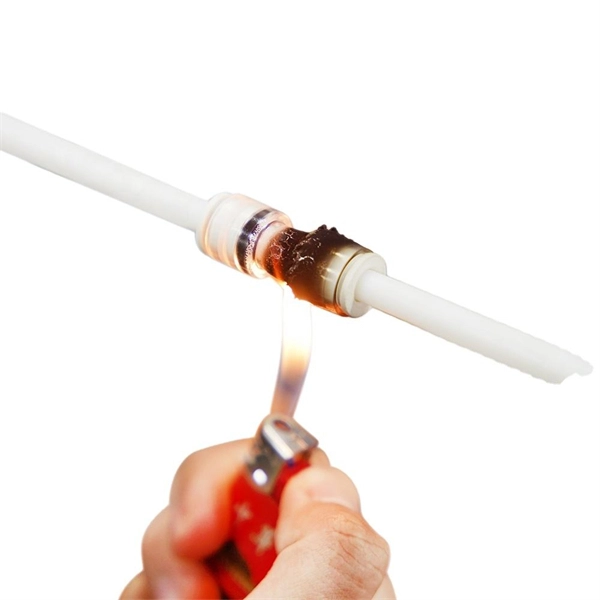
FTTR, or Fiber to the Room, is a networking technology that extends fiber optic connectivity directly into every room of a home or office. Invisible cable technology represents a groundbreaking advancement in the realm of fiber optics. These cables maintain the same high-speed data. Unlike standard drop cables (often GJXH or GJYXFCH) which are bulky and opaque, invisible fiber optic cable is a micro-diameter optical cable designed for discreet indoor deployment. It is designed to offer seamless data transfer and power supply while minimizing the visual clutter associated.